When Your AI Coding Assistant Becomes the Attack: The Hades Supply Chain Campaign - Morphisec
When Your AI Coding Assistant Becomes the Attack: The Hades Supply Chain Campaign Morphisec
Topics: Code Assistants
Entities: Code Assistants
Community feed
A focused stream of recent stories from the sources curated for this community. Latest: When Your AI Coding Assistant Becomes the Attack: The Hades Supply Chain Campaign - Morphisec, Spreading the load: How Salesforce met Multi-AZ HA with SageMaker Inference Components, and New sequential recommender tops most benchmark tests. Page 230.
When Your AI Coding Assistant Becomes the Attack: The Hades Supply Chain Campaign Morphisec
Topics: Code Assistants
Entities: Code Assistants
Learn how Salesforce used Amazon SageMaker AI Inference Component placement (the SchedulingConfig parameter) to distribute model copies across multiple Availability Zones, meeting their Multi-AZ high availability compliance requirements without sacrificing...
A preprint reports that HSR led most sequential-recommendation metrics and outperformed Mamba4Rec on several Amazon-Beauty efficiency measures.
How to run the backend locally with Docker or in the cloud
A preprint reports a compact AI model using less sampling compute and scoring better on two satellite-to-radar benchmarks, but running slower.
Windows 11’s optional August update has a cursor bug. Skip it for now PCWorld
Topics: IDEs
Claude Code runs malware despite “Auto Mode” security, tries to fix it, gets denied Cybernews
Topics: Code Assistants
Entities: Code AssistantsClaudeClaude Code
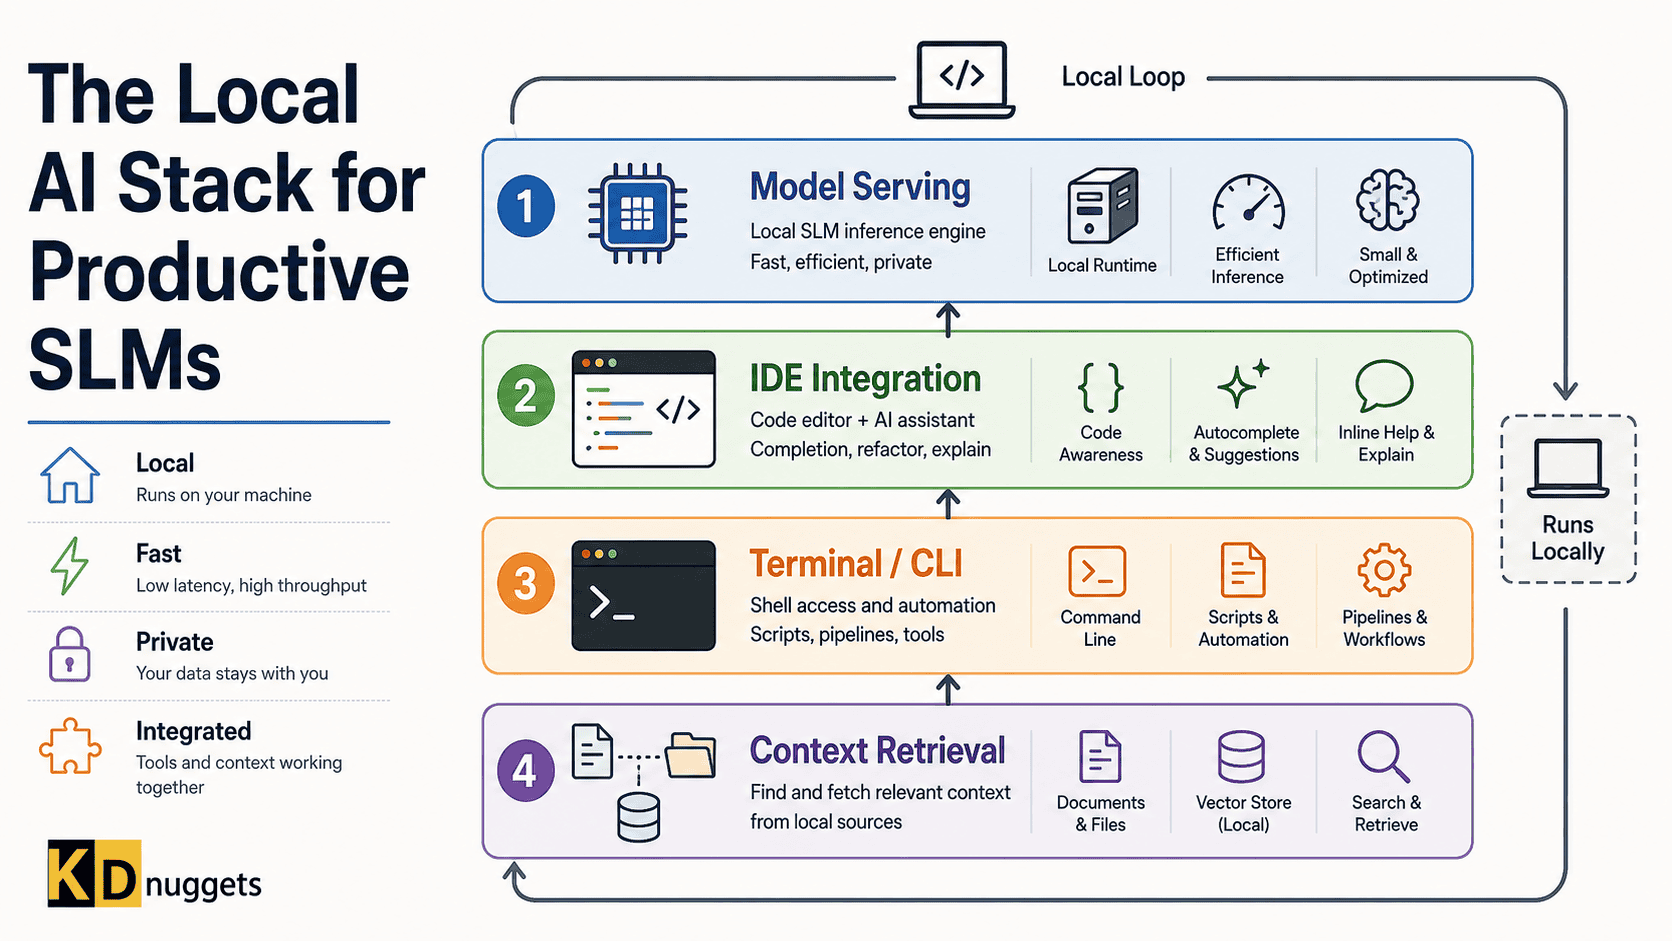
A practical framework for choosing the right tools at each layer of your local AI setup, from model serving to context retrieval.
Be a better communicator with LLM programming
Topics: Code Assistants
Entities: Code AssistantsClaudeClaude Code
With GitHub Copilot Integration, Teams Powers Greater Developer-Agent Collaboration Cloud Wars
Topics: Coding AgentsCode Assistants
Hackers from the Russian-speaking group Aur0ra used Cursor AI to hack at least 10 companies Mezha
Topics: IDEs
A preprint reports an evidence-using LLM system led CVSS vulnerability-rating tests, but a small user study and label limits temper the result.